Security
Web Security for Developers: The Essentials You Can't Skip
The security vulnerabilities that appear most often in web applications, explained with real code examples and concrete fixes every developer should know.
·3 min read
Tags
12 articles
The security vulnerabilities that appear most often in web applications, explained with real code examples and concrete fixes every developer should know.

Protect API keys in frontend applications with backend proxies, token vaulting, environment hygiene and runtime injection — never in a browser bundle.

Implement OAuth 2.0 and OpenID Connect correctly: authorization code flow with PKCE, token management, refresh rotation and the pitfalls behind takeovers.

Zero-trust networking from an application developer's view: mutual TLS, service mesh authentication and request-level authorization for every call.

A practical guide to choosing and implementing secure authentication for modern APIs: JWT tokens, OAuth 2.0 flows and session management pitfalls.

Secure OAuth 2.0 token lifecycle management: storage strategies, automatic rotation with refresh tokens, revocation propagation and replay protection.

A practical guide to securing APIs with token-based auth, role-based access control, scope permissions and API key management — plus common pitfalls.

What zero trust means beyond the buzzword: identity-based access, mutual TLS, network microsegmentation and applying it at the application layer.

A complete guide to understanding and preventing CSRF attacks: token-based protection, SameSite cookies, double-submit and framework implementations.

JWTs are deceptively simple — here's how to avoid the security vulnerabilities, performance traps, and architectural mistakes that plague most implementations.

Authorization Code, PKCE, Client Credentials — which OAuth flow to use for which application type, and the security pitfalls hiding in each one.
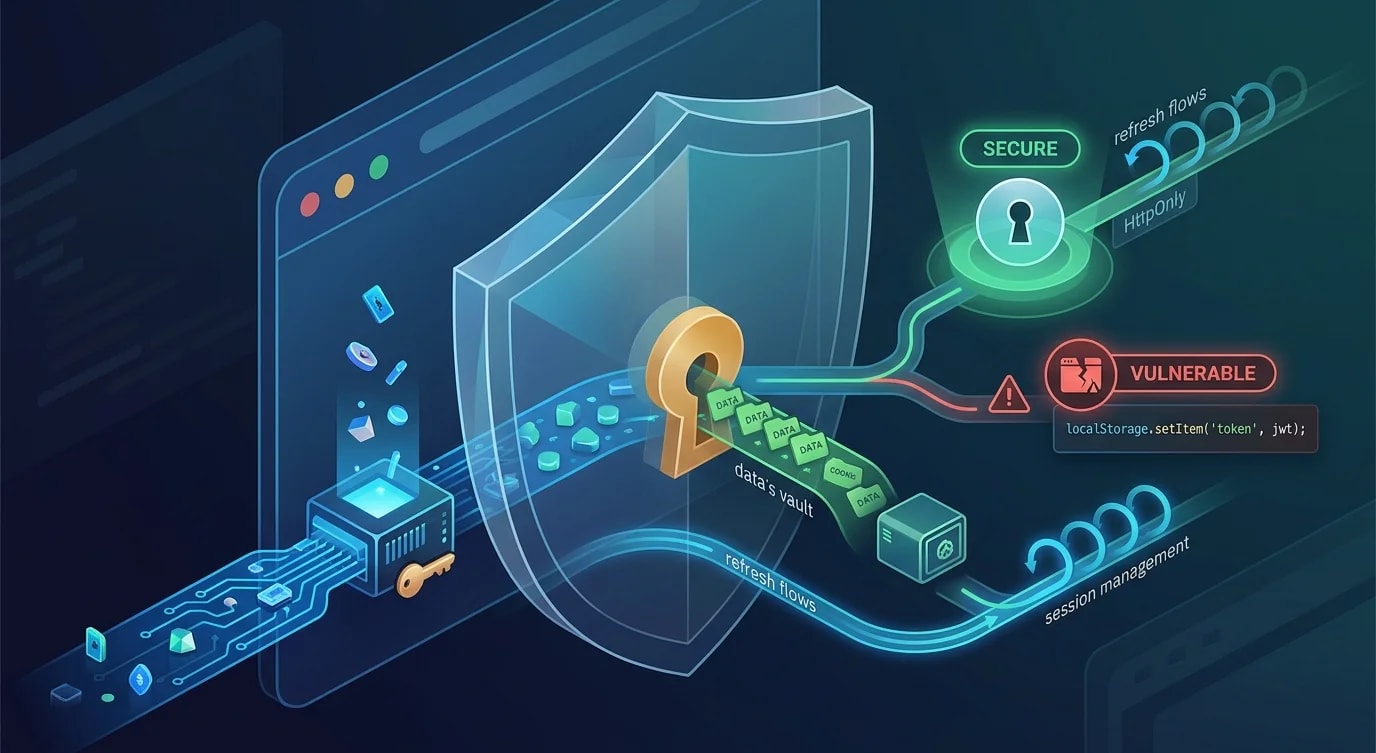
Tokens, cookies, refresh flows, and session management — the authentication patterns that keep SPAs secure without sacrificing user experience.