
Security
Cross-Site Request Forgery Protection Strategies
A complete guide to understanding and preventing CSRF attacks: token-based protection, SameSite cookies, double-submit and framework implementations.
·5 min read
Tags
2 articles
A complete guide to understanding and preventing CSRF attacks: token-based protection, SameSite cookies, double-submit and framework implementations.
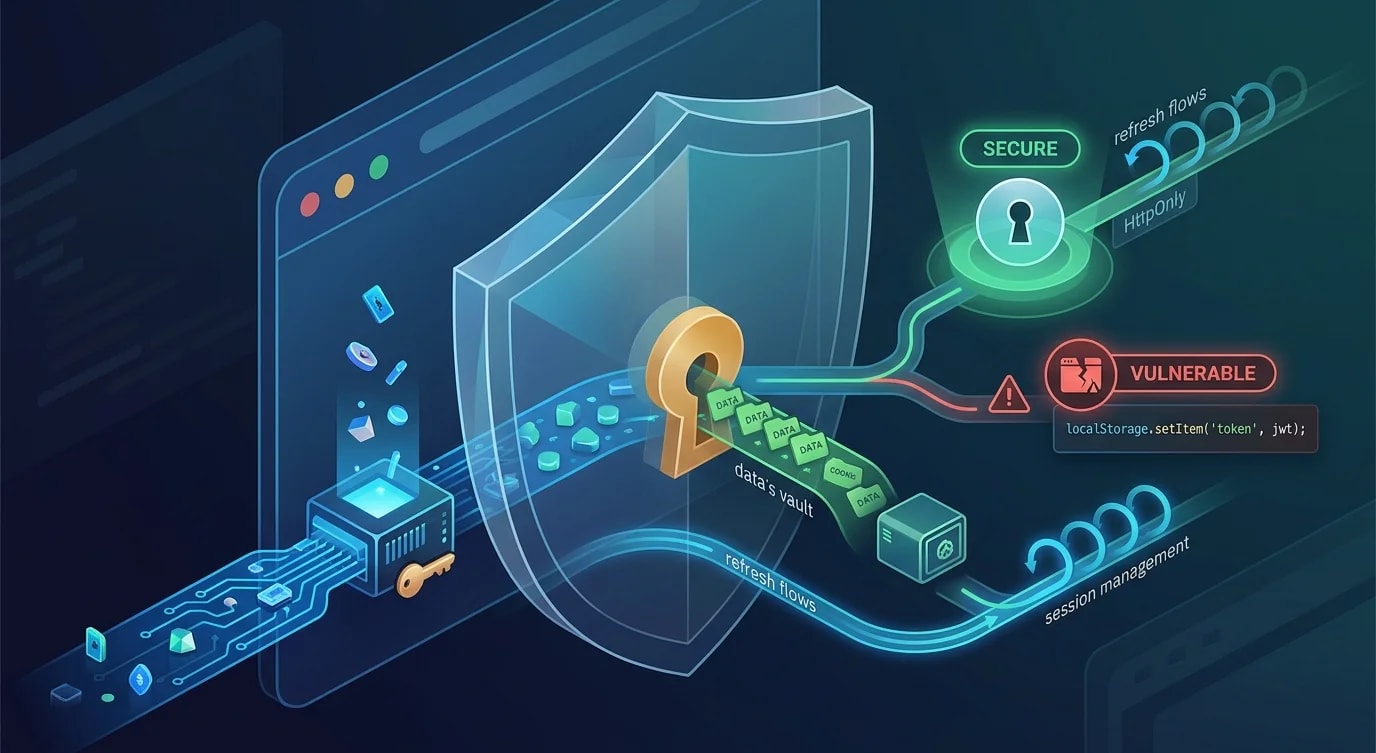
Tokens, cookies, refresh flows, and session management — the authentication patterns that keep SPAs secure without sacrificing user experience.