Security
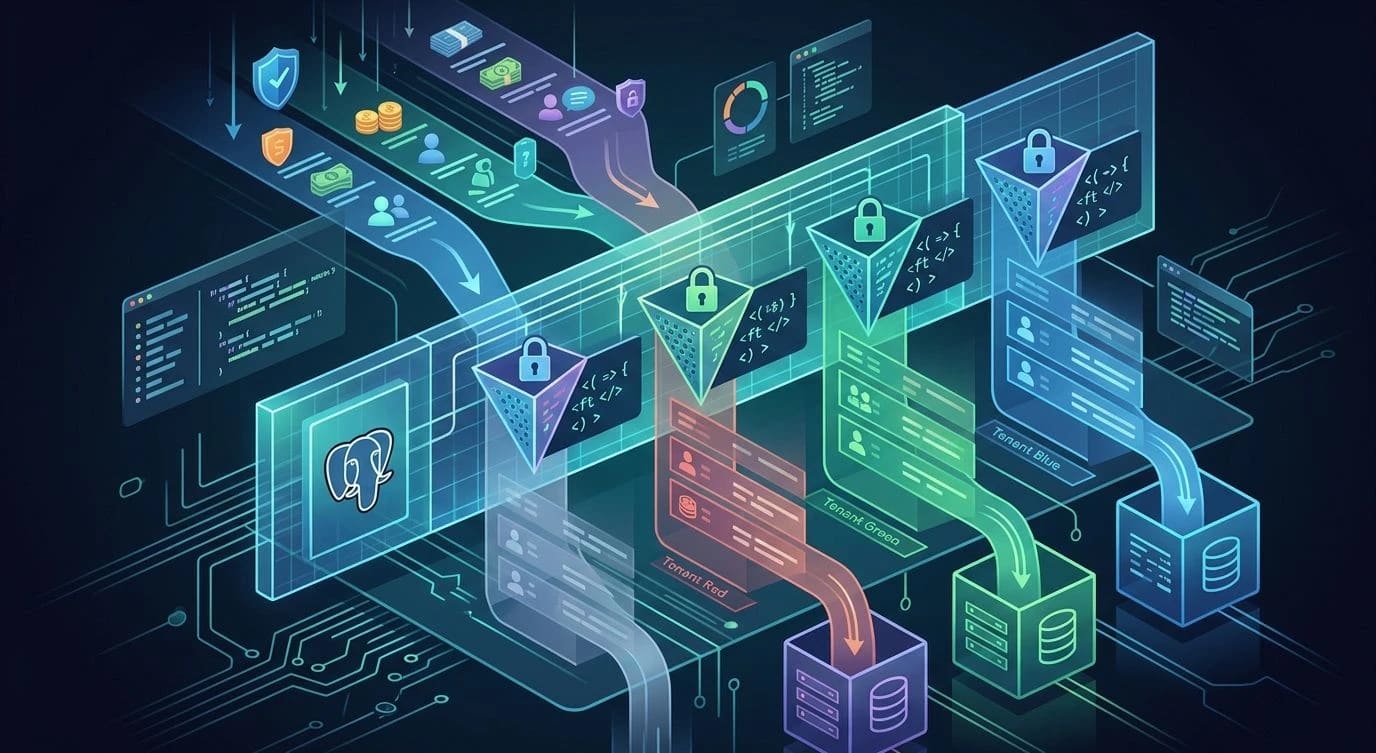
Postgres Row-Level Security for Multi-Tenant Applications
How to enforce tenant isolation at the database layer with Postgres RLS instead of relying on application code to remember a WHERE clause.
·4 min read
Categories
Vulnerabilities & defenses · 31 articles · Page 1 of 3
How to enforce tenant isolation at the database layer with Postgres RLS instead of relying on application code to remember a WHERE clause.
The security vulnerabilities that appear most often in web applications, explained with real code examples and concrete fixes every developer should know.

Protect API keys in frontend applications with backend proxies, token vaulting, environment hygiene and runtime injection — never in a browser bundle.

Implement OAuth 2.0 and OpenID Connect correctly: authorization code flow with PKCE, token management, refresh rotation and the pitfalls behind takeovers.

Zero-trust networking from an application developer's view: mutual TLS, service mesh authentication and request-level authorization for every call.

A security guide to defending LLM-integrated applications against prompt injection: input sanitization, output validation, privilege separation, blast radius.
A complete guide to securing your software supply chain: dependency auditing, lockfile integrity, build hardening, SBOM generation and artifact provenance.

The security challenges unique to serverless: injection through event sources, over-permissioned functions and dependency risk, with practical mitigations.

A complete guide to protecting your software supply chain from dependency confusion, typosquatting, compromised packages and build pipeline attacks.

A practical guide to choosing and implementing secure authentication for modern APIs: JWT tokens, OAuth 2.0 flows and session management pitfalls.

Protect credentials in CI/CD pipelines with secret managers, environment isolation, least-privilege access and audit trails — without slowing deploys.
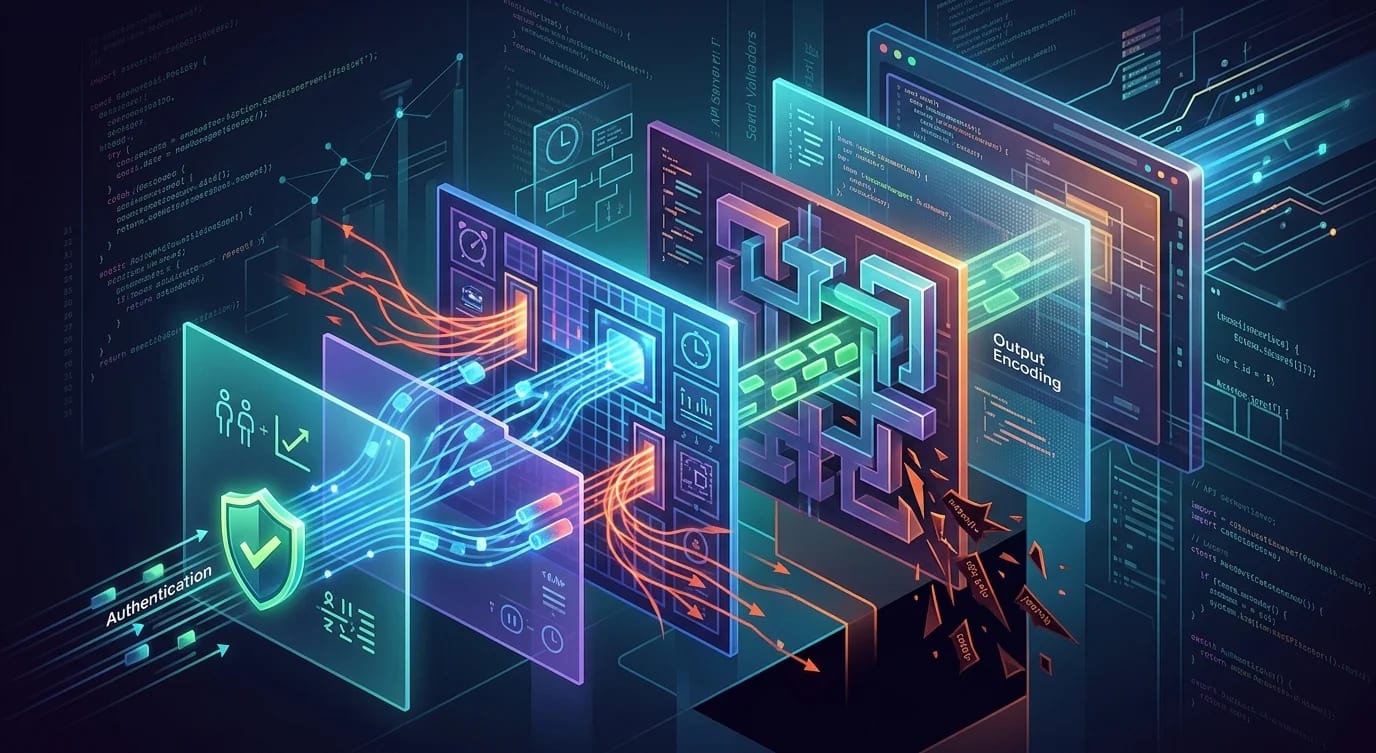
API security layers beyond auth: rate limiting, request validation, output encoding, security headers and audit logging, with TypeScript middleware.