
Security
Supply Chain Security for Software Dependencies
Protect your supply chain with dependency pinning, lockfile integrity checks, SBOM generation, automated scanning and third-party risk monitoring.
·4 min read
Categories
Vulnerabilities & defenses · 31 articles · Page 2 of 3
Protect your supply chain with dependency pinning, lockfile integrity checks, SBOM generation, automated scanning and third-party risk monitoring.
Robust secrets management with HashiCorp Vault, AWS Secrets Manager and sealed secrets: rotation, injection, least privilege and no secret sprawl.

Secure OAuth 2.0 token lifecycle management: storage strategies, automatic rotation with refresh tokens, revocation propagation and replay protection.

Runtime security patterns that detect and block attacks from inside your Node.js application: SQL injection detection, path traversal and anomaly alerting.

Robust API authorization with RBAC, ABAC and policy-as-code — protecting resources at every layer while staying maintainable as the system grows.
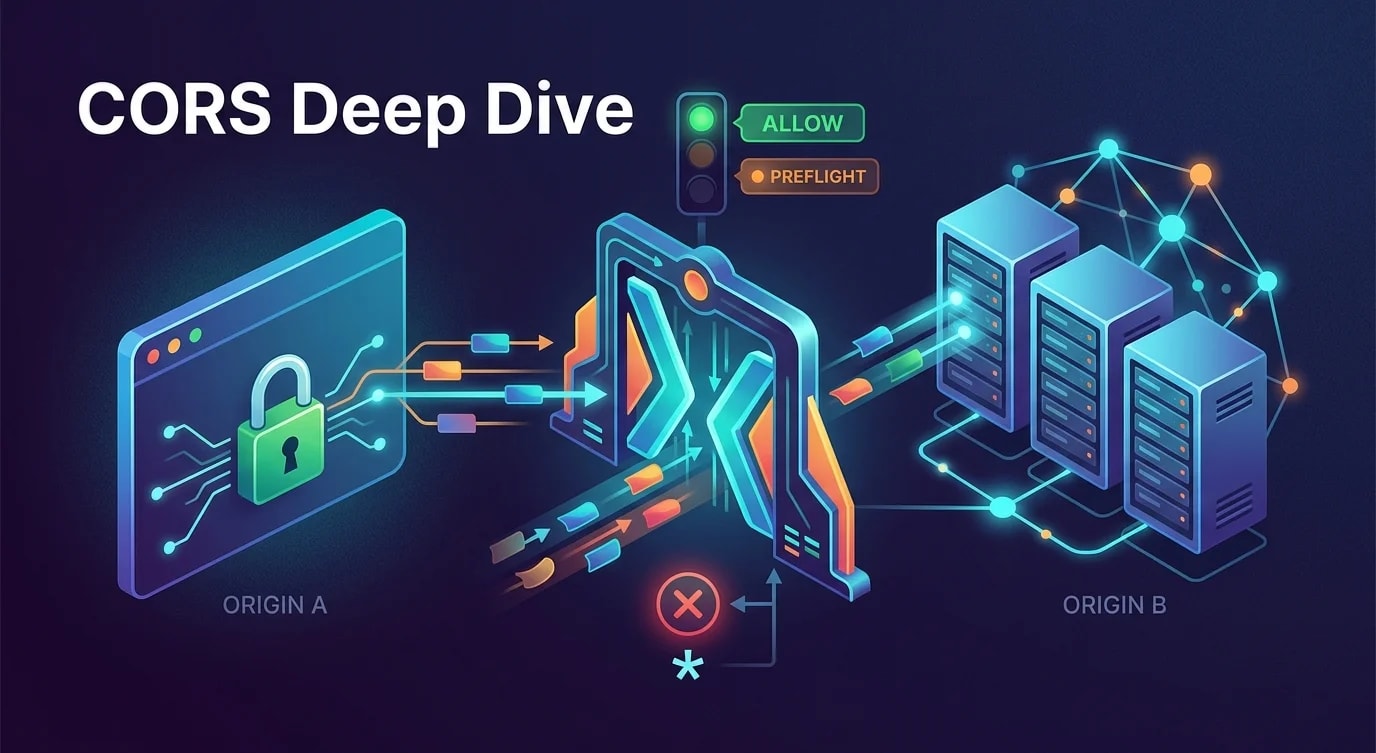
Understand how CORS actually works at the protocol level and implement secure, correct configurations that don't resort to wildcard allow-all patterns.
Understand the security challenges unique to serverless architectures and apply practical defense patterns for AWS Lambda, Azure Functions and friends.

How to implement Content Security Policy headers that actually protect you: directive syntax, nonce-based inline scripts, reporting and safe rollout.

Practical techniques for hardening Docker containers: image scanning, least-privilege configuration, secrets, network policies and runtime monitoring.

A practical guide to securing APIs with token-based auth, role-based access control, scope permissions and API key management — plus common pitfalls.

What zero trust means beyond the buzzword: identity-based access, mutual TLS, network microsegmentation and applying it at the application layer.

How to protect JavaScript projects from supply chain attacks: dependency auditing, lockfile integrity, typosquatting detection and CI vulnerability scans.